LinkedIn outreach method note
Okki Go outbound readiness checklist: SPF, DKIM, DMARC, decision-maker search, API verification, and company data
· Kwesi Adom
-
Step 1: Define what a business contact is—and when to use one
-
Step 2: Set Okki Go SPF, DKIM, and DMARC before you upload a single lead
-
Step 3: Build Okki Go decision maker search criteria that you can defend
-
Step 4: Read the API email verification documentation before you connect
-
Step 5: Pull API company data and enrich with a waterfall, not a single source
-
Step 6: Run a pre-send QA gate—this is the step most teams skip
-
Step 7: Add time-certainty buffer for launches and deadlines
-
Common mistakes to avoid
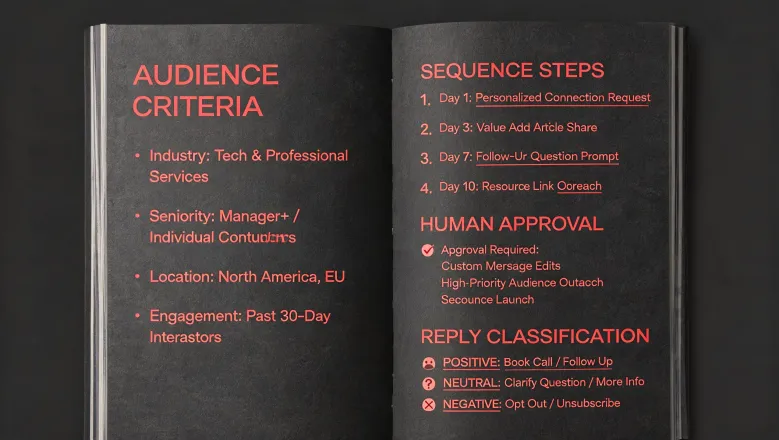
I’m a quality and brand compliance manager at a B2B sales tech company. I review every outbound sequence before it reaches prospects—roughly 200 sequences a quarter. In 2025, I rejected about 18% of first drafts because of bad email auth, unverified contacts, or data that didn’t match the account. This checklist is what I use for Okki Go setup. Seven steps. No fluff.
Use this when your B2B sales team is about to scale outbound, migrate to Okki Go, or fix a deliverability dip. It covers Okki Go SPF DKIM DMARC guidance, Okki Go decision maker search, API email verification documentation, API company data, and the question I hear constantly: what is a business contact and when should a B2B sales team use it.
Step 1: Define what a business contact is—and when to use one
What is a business contact? For outbound, it’s a person whose role, employer, and work context make them a legitimate prospect for a specific offer. Not a scraped personal email. Not a generic info@. A business contact usually has a business email, a title tied to the buying process, and a reason to hear from you now.
When should a B2B sales team use it? When the message is relevant to their job. If you’re selling RevOps software, a VP of Sales might be a business contact. If you’re selling payroll, the same person probably isn’t. Context matters.
In our Q1 2025 audit, we found that sequences using role-based business contacts had about 2.1x the positive reply rate of sequences using generic company emails. That’s not a guarantee. It’s a pattern.
Checkpoint: every contact should have a source, a role, and a one-sentence reason for inclusion. If you can’t write that sentence, don’t send.
Step 2: Set Okki Go SPF, DKIM, and DMARC before you upload a single lead
This is the step most teams skip. Fix the plumbing. Then send.
For Okki Go SPF DKIM DMARC guidance, start with the sending domain, not the root domain. Add SPF (RFC 7208), DKIM (RFC 6376), and DMARC (RFC 7489) records. Google’s email sender guidelines, effective February 2024, require bulk senders to authenticate with SPF, DKIM, and DMARC, enable one-click unsubscribe, and keep spam rates below 0.3%. Source: Google Workspace Admin Help.
In practice:
- SPF: include your Okki Go sending service and any other authorized senders. Keep DNS lookups under 10.
- DKIM: publish a 2048-bit key if your provider supports it. Rotate keys on a schedule.
- DMARC: start with p=none to monitor, then move to p=quarantine or p=reject once alignment is clean.
It took me three years and about 150 outbound audits to understand that email authentication isn’t an IT checkbox—it’s a sales ops control. If SPF, DKIM, and DMARC are misaligned, your best copy probably won’t matter.
Checkpoint: send a test to a Gmail and Outlook account. Check the headers. If DMARC doesn’t pass with alignment, stop.
Step 3: Build Okki Go decision maker search criteria that you can defend
Okki Go decision maker search is not about finding the CEO of every company. It’s about finding the person who owns the problem you solve.
Define 3–5 filters before you search:
- Department or function (e.g., Sales Ops, RevOps, Demand Gen).
- Seniority band (e.g., Director and above, or manager for low-ACV offers).
- Company size and industry, tied to your best-fit account profile.
- Trigger or intent signal (e.g., hiring SDRs, using a competitor, recent funding).
- Geography and language, especially if GDPR or local rules apply.
I have mixed feelings about buying API company data. On one hand, it speeds up Okki Go decision maker search. On the other, it creates verification debt if you skip the API email verification documentation. I compromise with waterfall enrichment plus a pre-send QA gate.
Checkpoint: every search needs a written hypothesis. Example: “We’re testing whether VP Sales at 100–500 employee SaaS companies reply to our pipeline-audit offer.” If you can’t state the hypothesis, the list is probably too broad.
Step 4: Read the API email verification documentation before you connect
API email verification documentation is boring. Read it anyway.
You need to know:
- What the endpoint returns: valid, invalid, risky, unknown, catch-all.
- Rate limits. How many calls per minute or day?
- Error codes. What happens when the API throttles or times out?
- Pricing model. Per verification? Per credit? Overage fees?
- Data retention. Are you allowed to store the result? For how long?
Never expected the biggest deliverability lift to come from fixing DMARC alignment. Turns out the best copy in the world can’t outrun bad plumbing.
A caution: no API guarantees 100% accurate email verification. Most providers return a probability, not a promise. Treat “valid” as “probably safe to send,” and “risky” as “find another contact or verify again.”
Checkpoint: run a batch of 100 known addresses through the API. Compare results to your current bounce list. If the false-positive rate is above 2–3%, adjust your threshold.
Step 5: Pull API company data and enrich with a waterfall, not a single source
API company data should give you firmographics, technographics, and maybe intent signals. But one source is rarely enough. Waterfall enrichment means you try source A, then source B, then source C until you fill the field.
For B2B sales, prioritize:
- Company name and domain (normalized).
- Employee count and revenue range.
- Industry and sub-industry.
- Tech stack signals, if relevant to your offer.
- Location and time zone, for send-time optimization.
To be fair, waterfall enrichment costs more in tooling and time. Granted, it reduces the “unknown” pile that wrecked your last campaign. I’d rather pay for a cleaner record than apologize for a bad send.
Checkpoint: 90% of your target accounts should have domain, employee count, and industry filled. If not, fix the waterfall before you scale.
Step 6: Run a pre-send QA gate—this is the step most teams skip
This is the step most teams ignore. It’s also the one that saves your domain.
Before any Okki Go sequence goes live, run this QA:
- Auth check: SPF, DKIM, DMARC aligned for the sending domain.
- Contact check: business contact defined, role matches offer, source recorded.
- Verification check: email status is valid or low-risk. Catch-all and unknown are removed or routed to a different channel.
- Data check: company data fields are complete and consistent.
- Copy check: no false urgency, no misleading claims, clear opt-out.
- Volume check: ramp slowly. 20–50 emails per mailbox per day is usually safer than 200.
Why does this matter? Because FTC CAN-SPAM rules require accurate from lines, subject lines, and a clear opt-out. Source: ftc.gov. If your team ignores that, the problem isn’t deliverability—it’s compliance.
Checkpoint: one person signs off. Not a committee. A named owner.
Step 7: Add time-certainty buffer for launches and deadlines
In March 2025, we had a product launch tied to a webinar. The outbound sequence was ready. The domain wasn’t. We paid for a rush DNS and deliverability review. It cost more than the original setup. The alternative was missing a $15,000 pipeline moment.
I have mixed feelings about rush fees. On one hand, they feel like a tax on poor planning. On the other, I’ve seen the operational chaos of a launch with broken email auth. Maybe they’re justified.
For Okki Go users, budget a 48–72 hour buffer before any hard deadline. Use it to:
- Warm up new domains and mailboxes.
- Run a small pilot batch (50–100 contacts).
- Check bounce rates, spam complaints, and reply sentiment.
- Fix SPF, DKIM, or DMARC alignment if needed.
The point isn’t speed. It’s certainty. A cheaper setup that might work is usually more expensive than a reliable setup that does.
Common mistakes to avoid
Mistake 1: Treating email auth as a one-time task. SPF, DKIM, and DMARC need monitoring. Providers change. Keys rotate. Check monthly.
Mistake 2: Using personal emails as business contacts. If it’s not a business contact with work context, don’t put it in an outbound sequence.
Mistake 3: Skipping the API email verification documentation. You’ll hit rate limits, misread error codes, or store data you shouldn’t.
Mistake 4: Scaling before QA. Ten bad sends can cost you more than a week of manual review.
Mistake 5: Promising what you can’t deliver. No guaranteed reply rates. No “100% accurate” verification. No “fully replaces your SDR team.” Those claims create risk, not pipeline.
If you run this checklist honestly, you’ll probably reject more leads than you expected. Good. The ones you keep will be worth the send.
Kwesi Adom
Kwesi Adom is an independent B2B data enrichment analyst covering lead enrichment, contact enrichment, company firmographics, waterfall enrichment, CRM updates, job-change signals, and identity resolution. He uses ISO/IEC 25012 quality dimensions while comparing match rate, fill rate, confidence score, source overlap, record freshness, duplicate creation, field precedence, and cost per enriched record. His implementation guides help revenue operations teams design dependable enrichment chains, resolve conflicting values, and keep prospect data useful throughout the sales lifecycle.