LinkedIn outreach method note
Okki Go vs Artisan AI: A $31K RevOps Mistake Taught Me to Check Permissions and API Email Verification Docs
· Julian Hartwell
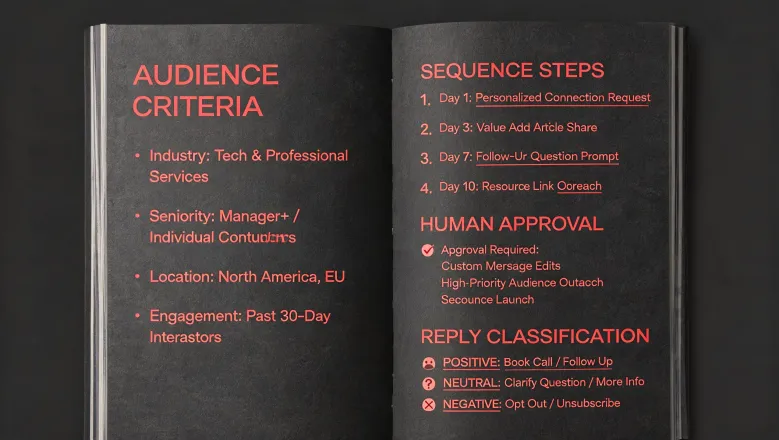
Short version: After roughly $31,000 in wasted AI-SDR spend, honestly, I no longer ask 'Okki Go vs Artisan AI, which is better?' I ask two much more boring questions: what permissions does this tool actually need, and can I read the email verification API documentation without being embarrassed for the vendor? The boring questions are the ones that save money.
For our team, a mid-market B2B company with existing SDRs and a CRM we're not willing to let an AI black box mess up, Okki Go was the better fit. That's not because Okki Go's feature list was longer. It's because its agent-native prospecting model, waterfall enrichment + intent data, and human-in-the-loop approvals fit how RevOps actually runs at our size. Artisan AI is a genuinely strong product if you want an autonomous AI SDR to own a sequence end-to-end. We just decided we don't. That distinction matters more than any 'winner' a review site will give you.
I'll unpack the comparison, answer the permissions question directly, and then share the API email verification documentation checklist we now use. If you're evaluating any prospecting tool, this should save you at least one mistake.
Why I started documenting my own AI-SDR mistakes
I'm a RevOps lead. I've been handling AI sales prospecting and outreach tooling for about three years. In that time I've made four significant mistakes that, all together, cost us around $31,000 in software commitments, wasted implementation time, and at least one compliance headache. I'm not telling you this because I think my experience is special. I'm telling you because the mistakes were almost all the same mistake: we evaluated the demo instead of the integration.
The trigger event was in February 2024. We signed a one-year AI-SDR contract after a demo where the sequences looked flawless. I clicked through the OAuth permission screen without really reading it: I remember thinking, 'this is just connecting our inbox, right?' Then our security team reviewed the access scope and pushed back hard. Two months and several legal emails later, we still hadn't run our first campaign. We had paid for the year though.
That's when our team started building the checklist I now maintain. It currently has 17 items. Items about permissions, about API documentation, about where data comes from, and about what happens when a tool says 'verified.' We've caught 13 problems with it since 2024. Some were minor. Some would have been expensive.
Okki Go vs Artisan AI: what the comparison actually taught us
During our last evaluation, we took both Okki Go and Artisan AI through the checklist. Both products are capable. The difference wasn't in the feature demos; it was in the mental model of where the AI sits in the workflow.
Artisan AI is basically an AI SDR worker. It wants to own the outreach motion—research, sequence, follow-up—and present you with a finished result. That's a legitimate and useful model for small teams that don't have bandwidth to supervise every touch.
Okki Go is closer to an agent-native prospecting layer for your existing revenue stack. It researches, enriches, verifies, and drafts, but the human stays in the loop on the parts that create risk—like actually sending from a rep's mailbox or touching a LinkedIn account. The waterfall enrichment and intent data are handled transparently, which made our security review more comfortable.
If you're a founder-led sales operation and want maximum autonomy, Artisan might be the right pick. If you're a RevOps team with established SDRs and compliance constraints, Okki Go's human-in-the-loop model is probably a better match. I recommend it for that scenario. But if you already have an enterprise security team that will reject anything with broad mailbox permissions, no tool is an easy sale—including Okki Go.
One more point on the comparison: both use intent data, but intent data is only useful if you know where it comes from and how often it's refreshed. We audit every vendor's intent data by asking for a sample of 100 records and spot-checking whether the contacts are still in role and their companies still fit our ICP. It's boring, but it's how we avoided buying a database of job-changed ghosts. (Note to self: we still need to write this audit process down somewhere easier to share.)
What permissions does Okki Go require? The specific answer
Okki Go doesn't install like a shady browser toolbar. The permission model depends on which connectors you enable, and exact scope names can change between plans—so don't hold me to the screenshots from our security review. But after going through the review, I can give you the practical breakdown.
1. Mailbox access (OAuth connection to Gmail or Microsoft 365). The outreach engine needs to send and read email on behalf of the connected mailbox. That includes reading replies so the AI can detect interest and update the sequence. The scope is roughly similar to what you'd grant your CRM or your current email-sending tool; it's not a 'full admin' role, but it is real access to your inbox.
2. CRM API access. You'll connect Okki Go to a CRM like Salesforce or HubSpot. The connector needs to create and update leads, contacts, and tasks. If you don't want an AI tool writing to your CRM without review, you'll want to disable auto-sync and use the human-in-the-loop features instead. That's a decision, not a default.
3. LinkedIn access (optional). If you run LinkedIn outreach, there's an extension component that works from the logged-in user's profile. This is where we were most cautious. It doesn't use a backend LinkedIn API the way it uses Gmail's API; it operates through the rep's browser session. That means your reps' LinkedIn accounts carry some risk, so decide who can enable it and on what kind of profile.
The surprise wasn't the length of the permission list. It was how much easier the conversation became when a vendor organized those permissions into clear categories. Okki Go's documentation made it simple for our security team to understand what was requested and why. Compare that with vendors whose docs are a wall of legal jargon, and you'll see why I call documentation a feature.
And again: if you're evaluating this, don't just ask 'does it need access to my email?' Ask for the exact OAuth scopes and take them to your security team before you sign anything. I learned that one the expensive way.
What should revenue operations teams evaluate in API email verification documentation?
Here's the part I really wish I had understood earlier. Email verification is not a binary yes/no thing. It's a probability judgment, and the API documentation is where the vendor admits how they handle that judgment.
Our old tool claimed to verify emails, but the API only returned 'valid' or 'invalid.' There was no middle ground. We learned the hard way that a huge portion of the email universe is catch-all, role-based, or just unknown—and pretending those are all 'valid' leads to bounces and burned sender reputation.
Now, when we evaluate any AI SDR or verification API, we check the documentation for these six things:
- Response categories beyond valid/invalid. Look for catch-all, role-based, disposable, temporary, and unknown states. Strong docs explain what each category means and how they recommend handling it. Weak docs pretend the world is binary.
- Error handling and rate limits. What happens when you hit a rate limit? Is there a 429 response with a retry header? Do the docs explain backoff? If not, prepare for integration pain.
- Batch and asynchronous options. For large lists, a synchronous per-email call isn't practical. We look for async job endpoints that let us submit a list and poll for results.
- Status 'unknown' guidance. Do the docs tell you not to send to unknown addresses? Do they recommend a secondary enrichment pass? A good verification API doesn't just give you false confidence with a 'valid' label.
- Data retention and privacy terms. Does the API store the emails you send it? For GDPR- and CCPA-sensitive RevOps teams, data retention and sub-processing terms should be findable in the docs or privacy policy.
- Cost semantics. Are credits consumed only on successful verification? What happens when a request errors or needs retry? This is where budget surprises are born.
If a vendor's API email verification documentation can't answer those six questions, I don't care how good their AI-generated opening lines are. The email infrastructure is the plumbing. If the plumbing leaks, everything downstream gets messy.
Also, don't let verification docs fool you into skipping email campaign compliance. The FTC's CAN-SPAM requirements still apply: every commercial email needs accurate header information, a clear subject line, a valid physical postal address, and a working opt-out mechanism that is honored within 10 business days. An email that has been 'verified' as deliverable is not an email that has consent to be sent. Your email campaign playbook should keep those rules separate from your verification workflow.
Where this checklist doesn't apply
One honest limit: this whole framework assumes you have a defined outbound motion and a CRM that's in decent shape. If your data is messy, if you have no SDR team, or if you're a three-person startup that just wants leads, a lighter-weight tool might make more sense. Okki Go and Artisan are both too much process for some teams.
In regulated industries, like healthcare or finance, you'll also need to check subprocessor lists and data processing agreements before signing. Our checklist surfaces those questions, but it can't answer them for your specific compliance team.
I still have mixed feelings about our $31,000 mistake. On one hand, it was avoidable and it still stings. On the other hand, the checklist it produced has saved us multiples of that by now. So maybe it wasn't entirely wasted. I just wish it hadn't required the tuition payment.
Julian Hartwell
Julian Hartwell is an independent B2B sales intelligence analyst covering contact databases, company data, decision-maker profiles, direct dials, prospect lists, and buying signals. He applies the ISO/IEC 25012 data-quality model while examining field accuracy, coverage, freshness, duplicate rate, match confidence, and source transparency. His evidence-led guides help revenue teams compare prospecting platforms, define acceptable data thresholds, and build account lists that support reliable territory planning and outreach.