LinkedIn outreach method note
Okki-Go's Permission Model Bets on Transparency — and That Sets the Bar for Every B2B Prospecting Tool
· Julian Hartwell
-
Here's my position: the biggest risk in B2B prospecting right now isn't cold emails getting flagged. It's that most teams don't actually know what permissions their tools get, where their B2B contact database records come from, or what "intent data" really means under the hood.
-
Permission scopes are the new pricing sheet
-
LinkedIn automation and the data source question nobody wants to answer
-
Intent data: use it when a signal changed, not when a signal exists
-
The awkward counterargument: "but the cheap tool works fine"
-
The bottom line
Here's my position: the biggest risk in B2B prospecting right now isn't cold emails getting flagged. It's that most teams don't actually know what permissions their tools get, where their B2B contact database records come from, or what "intent data" really means under the hood.
I run RevOps at a B2B outbound shop. Over the past six years I've coordinated 200+ campaigns, and a chunk of those were same-day scrambles — a client calls Friday afternoon, their SDR team needs 4,000 verified contacts by Monday 8am because a trade show just moved up.
So when a tool starts asking for OAuth scopes, or when a vendor hands me a contact list with no provenance, I notice. That's why the Okki-Go permission model caught my attention — not because it's generous, but because it's specific. More on that in a minute.
Permission scopes are the new pricing sheet
Everything I'd read about choosing a prospecting tool said to compare coverage, match rates, and price per contact. In practice, I've found that the first question that predicts whether a deal will go sideways is simpler: what does this thing actually ask for access to?
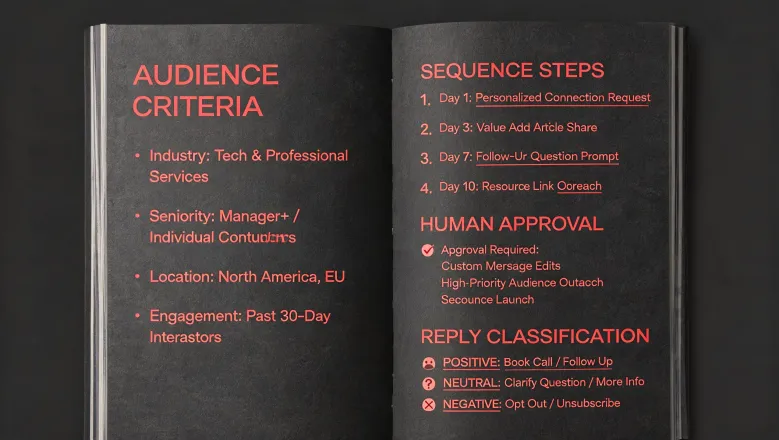
Okki-Go requires permissions tied to the sales workflow — LinkedIn connection data, mailbox send/read to run sequences, CRM write access for enrichment sync. That's the typical scope set. What matters is whether the vendor tells you why each scope is needed, and what happens when you revoke it.
I've personally tested tools that wanted inbox access and then never explained how they use historical email content. (Which, honestly, felt excessive.) And there's a difference between "we read subjects to detect replies" and "we index your whole sent folder for training." If a vendor can't articulate that line, the permissions page is fiction.
So the standard I'd apply to any tool — Okki-Go included — is this: every permission should map to a named feature, and revoking it should degrade a specific capability, not break your data. If it can't meet that, walk.
LinkedIn automation and the data source question nobody wants to answer
LinkedIn automation scraping is the elephant in every outbound room. Everyone does some version of it. Most vendors describe it with soft language. "Enriched from public sources." "Business contact intelligence."
The conventional wisdom is that as long as a vendor isn't explicitly using a banned third-party scraper, they're fine. My experience with 200+ campaigns suggests otherwise. What matters is disclosure granularity — whether the vendor tells you the difference between (a) first-party data they collected with consent, (b) data licensed from a broker, and (c) data inferred from pattern matching.
"LinkedIn doesn't publish an API that lets vendors scrape profiles at scale. Anything claiming otherwise is either licensed, inferred, or in a gray zone. Ask which one."
Per LinkedIn's User Agreement (last updated November 2024):
"You agree that you will not... use any robot, spider, scraper, or other automated means to access the Services for any purpose without our express written permission."
So when a vendor says they "integrate with LinkedIn", ask specifically what the integration surface is — official Marketing Developer Platform access, Sales Navigator seat access on your behalf, or something else. Those are three different risk profiles.
What Okki-Go gets right, from where I sit, is scoping its data source transparency into the product UI rather than burying it in a DPA addendum. You can see in the account view where a given record was enriched from. That's not a marketing claim I can verify for every record — I'm not 100% sure how deep the provenance chain goes for partner-sourced data — but the intent is correct, and intent compounds into trust.
Intent data: use it when a signal changed, not when a signal exists
This is where I'll be blunt, because I've watched too many SDR teams burn their quarter on this.
What intent data features actually do: they aggregate third-party signals — content pages read, review-site visits, job postings, tech-stack changes — and score accounts against a topic or category. Some tools layer first-party signals on top (email opens, site visits to your pricing page).
When a B2B sales team should use it: when the signal represents a change from the account's baseline, and when you have a hypothesis for why that change predicts a buying window. That's it. Not "they fit the ICP" — that's firmographic, not intent.
After five years of running outbound, I've come to believe that about 70% of the intent data most teams pay for is purchased and then never actioned, because nobody defined what "action" means. Say you score a mid-market SaaS account as "high intent" on CRM migration. Now what? Who emails them, with what offer, by when? If the answer is vague, the intent signal is theater.
Where intent data earns its keep in my shop is trigger-based: account posted a RevOps job req AND visited two comparison pages AND previously engaged with a competitor. Two out of three isn't intent. All three is a window.
The awkward counterargument: "but the cheap tool works fine"
I know how this reads. "Great, he's going to say you have to pay for the expensive option." That's not my point.
The cheapest B2B contact databases I've trialed sent me $60/month invoices and cost me hours of cleanup. Bounce rates north of 18%. Duplicate records across two exports from the same vendor. No field indicating whether the email was verified last week or last year. So the invoice was small, but the total cost of ownership — SDR time scrubbing, domain reputation damage, reply-rate hit — was way bigger than the subscription.
Then again, I've also been surprised. Last quarter I ran a small pilot comparing two mid-tier enrichment providers at very different price points. The cheaper one had a better match rate on EMEA mid-market, which is not what I expected going in. So the transparency logic isn't "expensive equals honest." It's:
- The provider who lists their sources, refresh cadence, and verification timestamps upfront — even if the price looks higher — usually costs less per usable record.
- The provider who hides that behind "AI-powered accuracy" is selling you the cleanup work later.
I've learned to ask "what's NOT included" before I ask "what's the price." That habit comes from getting burned, not from being wise.
The bottom line
Okki-Go as a case study matters less than the principle it reflects: permissions should map to features, data sources should be visible per record, and intent signals should trigger action or be ignored. If your current stack can't answer "where did this contact come from and what did my tool access to get it," it's not a data quality problem yet. It's a disclosure problem that becomes one.
I'm not 100% sure the whole industry will shift this way. Pricing pressure pushes the other direction — toward vague claims and bundled mystery data. But every RevOps lead I respect is asking the same questions now, and the tools that answer clearly are the ones that survive the next procurement review.
Take this with a grain of salt: my sample is one team, one vertical, one segment. But the direction of travel feels real. Pick the vendor that tells you what it's doing. Even when the answer is unflattering.
Julian Hartwell
Julian Hartwell is an independent B2B sales intelligence analyst covering contact databases, company data, decision-maker profiles, direct dials, prospect lists, and buying signals. He applies the ISO/IEC 25012 data-quality model while examining field accuracy, coverage, freshness, duplicate rate, match confidence, and source transparency. His evidence-led guides help revenue teams compare prospecting platforms, define acceptable data thresholds, and build account lists that support reliable territory planning and outreach.